Publication Date: 04 November 2026
Dear Customer,
CVE-2026-98432 is a security vulnerability identified in the Linux kernel, involving a use-after-free condition in IPv4 TCP processing. This is a broader Linux ecosystem security concern that is not limited to any particular vendor, product, or organization. It may affect systems and platforms worldwide running vulnerable Linux kernel versions. Under certain conditions, successful exploitation could potentially compromise the confidentiality, integrity, and availability of affected systems.
ANTlabs is aware of CVE-2026-98432. We take this matter seriously and have promptly evaluated the potential impact on our products, prioritizing the development and release of the necessary security updates.
SG5
- • SG5 Security Hotfix Update 19 (U19) has been released and includes the necessary remediation for these vulnerabilities.
- Please see this link for the release note: SG 5 Update #19
- Released on 3 November 2026
The updates apply to the following product:
- • SG Express 5000
- • SG Express 5100
- • SG Express 5200
- • SG Express 5200-10GE
- • vSG Express
- • SG Pro 5400
- • SG Pro 5410
- • vSG Pro
- • IG4 S-series (upgraded with v5 software)
Tru’IP
- • Tru’IP Gen5 Systems hotfix has been released and addresses the vulnerabilities.
- Released on 3 November 2026
Recommended Customer Action
Please take immediate action to schedule and apply the applicable security update
If you require assistance or need further clarification, please contact ANTlabs Technical Support.
24-hour hotline: +65 6100-7877
US customers: +1-904-430-8477
Email: tech-support@antlabs.com
Publication Date: 22 October 2026
Last Updated: 3 November 2026
Dear Customer,
ANTlabs is aware of the critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. We take this matter seriously and have promptly evaluated the potential impact on our products, prioritising the development and release of the necessary security updates.
Security Remediation Schedule
SG5
- • SG5 Security Hotfix Update 18 (U18) has been released and includes the necessary remediation for these vulnerabilities.
- Released on 22 October 2026
- Please see this link for the release note: SG 5 Update #18
The updates apply to the following product:
- • SG Express 5000
- • SG Express 5100
- • SG Express 5200
- • SG Express 5200-10GE
- • vSG Express
- • SG Pro 5400
- • SG Pro 5410
- • vSG Pro
- • IG4 S-series (upgraded with v5 software)
ASP
- • ASP 2.9.3, which includes the necessary security remediation,
- Released on 23 October 2026
- Please see this link for the release note: ASP 2.9.3
ANTlabsEzCast
- • ANTlabsEzCast Hotfix Update 6 has been released, incorporating the necessary fixes to address the vulnerabilities.
- Released on 23 October 2026
- Please see this link for the release note: ANTLabsEzCast Update 6
ACG
- • ACG Security Hotfix has been released and addresses the critical PHP vulnerabilities.
- Released on 30 October 2026
TruAuth
- • TruAuth CMS Security Hotfix has been released and addresses the critical PHP vulnerabilities.
- • TruAuth AAA and TruAuth ADC are not affected.
- Released on 30 October 2026
TruIP
- • TruIP CMS Security Hotfix has been released and addresses the critical PHP vulnerabilities.
- • TruIP DHCP and TruIP DNS are not affected.
- Released on 3 November 2026
Recommended Customer Action
Please take immediate action to schedule and apply the applicable security update
Please retain and refer to this advisory for the latest release schedule. We will update this advisory as new information and security updates become available.
If you have any questions, require clarification, or need assistance, please contact ANTlabs Technical Support:
24-hour hotline: +65 6100-7877
US customers: +1-904-430-8477
Email: tech-support@antlabs.com
Publication Date: 07 August 2025
Discontinuation of Advanced QoS Plus and Web-Filtering Modules on SG 5 Series
Overview
Effective August 01, 2025, ANTlabs will discontinue offering the Advanced QoS Plus module and Web-Filtering service for the SG 5 range of gateways.
This change affects only the Advanced QoS Plus and Web-Filtering optional add-ons. All other features — including standard QoS, access control functions, and the Advanced QoS module — will continue to be supported and available.
Key Points
Discontinued:
- Advanced QoS Plus module
- Web-Filtering service
Still available and supported:
- Standard QoS
- Access Control features
- Advanced QoS module (not affected by this change)
- Availability for Special Projects
Note: While these modules will no longer be bundled or offered by default in new SG 5 deployments, they may still be made available on a project basis upon request, subject to commercial and technical considerations.
Our Commitment
ANTlabs continues to deliver intelligent and scalable network management solutions. Though we are retiring selected optional modules, our team retains deep expertise in supporting traffic shaping and content control needs as required.
In line with our roadmap, we will be introducing new service modules and enhancements in the coming months to address the evolving needs of the hospitality industry.
Contact
For further clarification or to discuss your specific project needs, please reach out to your ANTlabs representative or contact us at:
📧 sales@antlabs.com
Publication Date: 30 Sep 2024
Key Changes in iOS 18
iOS 18 introduces a significant update in how devices manage MAC address randomization, enhancing user privacy. The feature, known as “Rotate Wi-Fi Address,” will change the MAC address of a device every 2 weeks. In the example below, the Private Wi-Fi Address setting for the particular Wi-Fi network has been set to “Rotating”, meaning that MAC Address randomization is enabled on the iOS device.
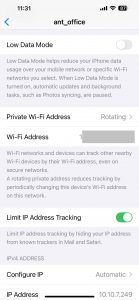
iOS 18 MAC Randomization Feature – Under Settings->Wi-Fi->
Click the “i” to see the “Private Wi-Fi Address” Setting
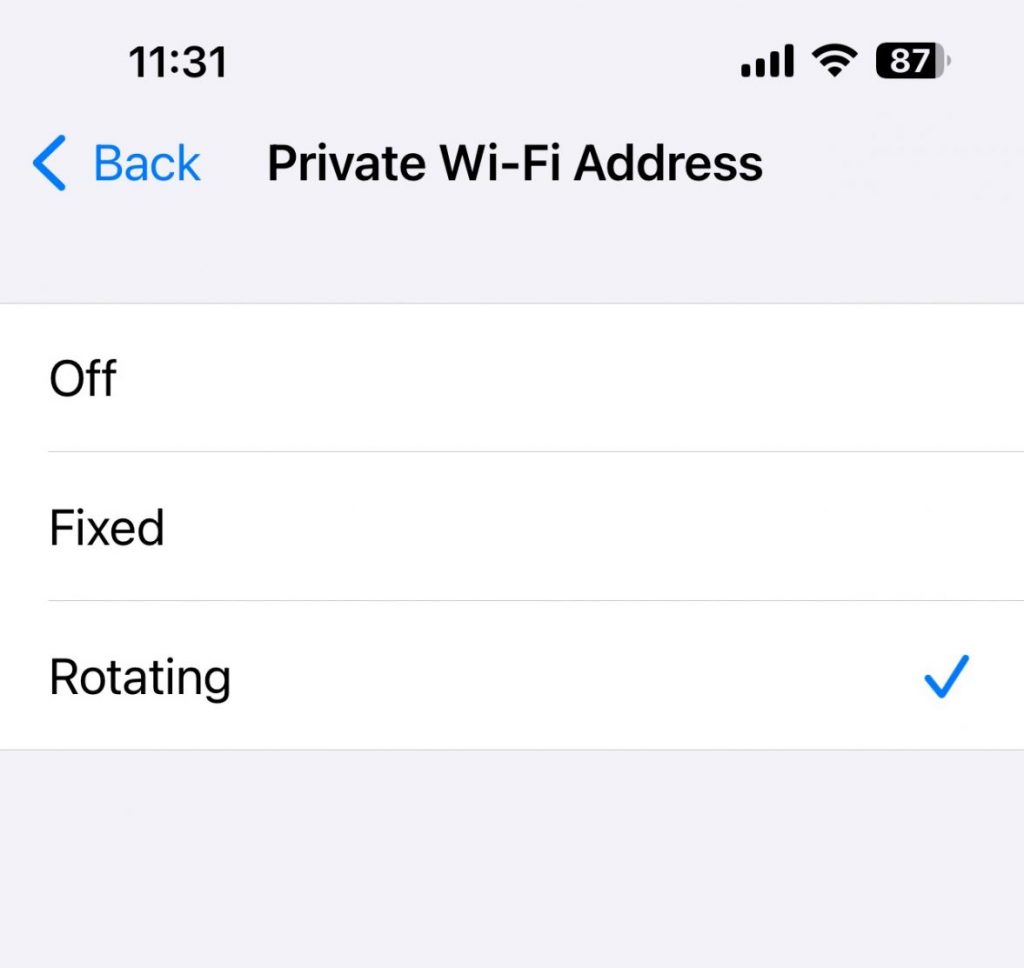
Rotating value indicates MAC Randomization in effect
Impact on Non-Secure SSIDs
For hotels offering public or guest Wi-Fi, this can create challenges. Guests who return after two weeks may experience login prompts as if they’re connecting for the first time. For long-stay guests, iOS 18’s MAC address randomization will cause them to see the login page again every two weeks, even if they’ve previously connected. As the network no longer recognizes their device, this disrupts what should be a seamless reconnection process.
Negative Effect on Guest Experience
Frequent re-authentication could frustrate returning guests, particularly those expecting uninterrupted access after an initial login. In an environment where guest satisfaction is paramount, these repeated prompts may lead to negative feedback, even though it’s caused by Apple’s privacy updates. Another critical issue is that hotel Wi-Fi networks lose the ability to retain their guest device and status recognition, preventing network services from providing differentiating services like higher bandwidth for elite members, or auto-completion of guest details and accord privileges reserved for elite members.
Solutions to Consider
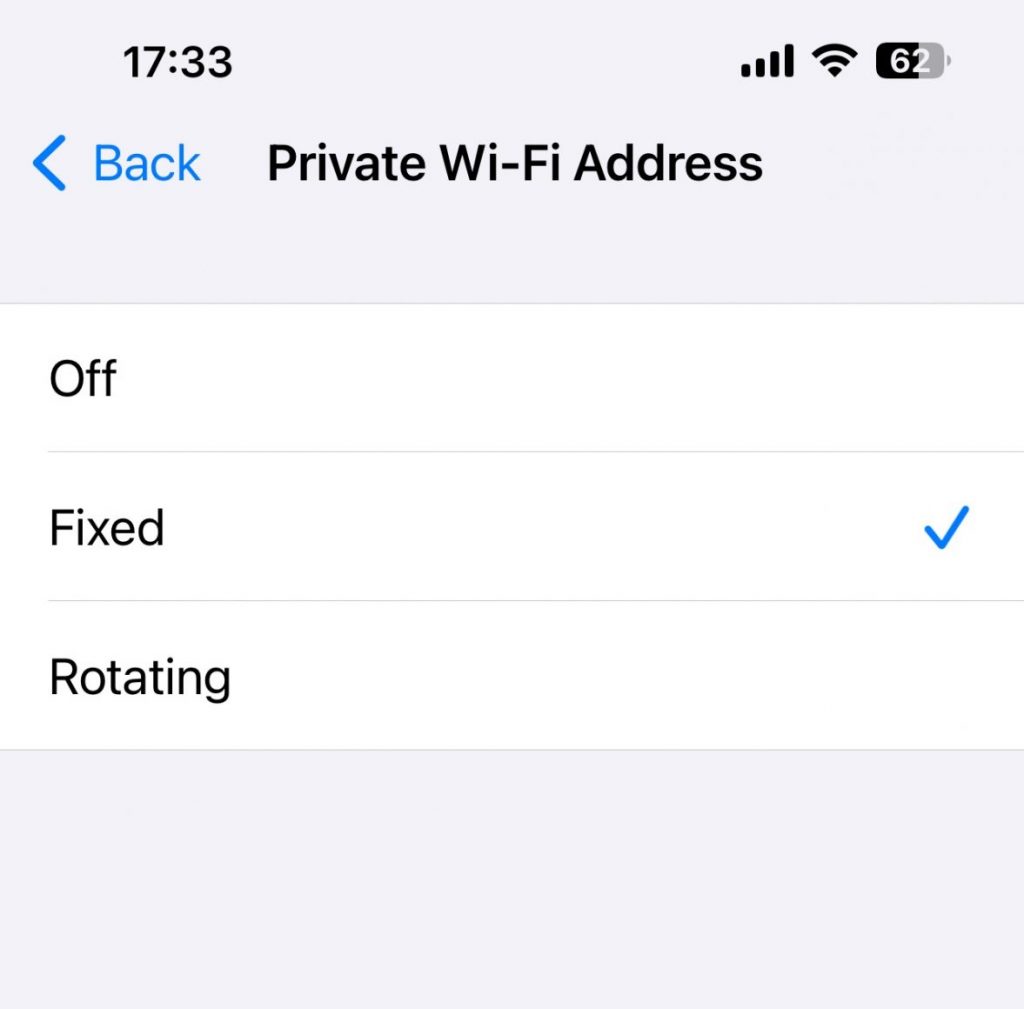 Short-Term Solution: Guests can disable MAC randomization for your network through their device settings, but this solution places the responsibility on them. To do so, guests can select “Fixed” under the Private Wi-Fi address setting.
A Long-Term Strategy: To mitigate these disruptions, consider integrating network solutions designed to handle iOS 18’s privacy features without affecting the guest experience. At ANTlabs, we specialize in networking solutions like Hotspot 2.0 or Wi-Fi profile that address these changes head-on, ensuring smooth and consistent connectivity for your guests while keeping their privacy intact.
Next Steps
Now is the time to explore more robust, long-term options. Contact ANTlabs to discuss how we can help your network adapt to these changes, improving both guest satisfaction and network management efficiency.
Talk to us to know more about ANTlabs Hotspot 2.0 solutions to solve the MAC Randomization issue.
Source: Apple Support – Use private Wi-Fi addresses on Apple devices (Scroll to the section “Learn how this feature works”)
-
Publication Date: 16 December 2021 We are aware of a new security vulnerability targeting the open source Log4j logging utility that was announced recently. The vulnerability allows hackers to execute malicious code on servers and client machines. ANTlabs products are not affected by this vulnerability as we do not use the Log4j logging utility. Please […]
-
The current ezxcess.antlabs.com SSL certificate on our gateways will expire on April 7, 2021. For HTTPS login pages that are served out with the ezxcess.antlabs.com SSL certificate, browsers will present certificate errors after April 7, 2021, if the SSL certificate expiry is not extended. Also, for deployments that integrate with the Accor FLINT-HTNG PMS, the […]
-
Last Updated: 15 Oct 2020Publication Date: 24 Sep 2020 What is Randomized MAC and what is it for? With the recent launch of IOS 14 and Android 10, a new feature is introduced which configures the phone to use a randomized MAC address when connecting to a WiFi network. The feature is enabled by default […]
-
Updated: 23 July 2020 We have added the walled garden HTTPS domains feature as the recommended approach to allow downstream devices to access the payment gateways before login. In doing so, we are effectively decommissioning the IP Address-based walled garden configuration. As such, it is advised to add the relevant HTTPS domains to the walled […]
-
Last Updated: Oct 15, 2020 – The Instagram WiFi login issue has been resolved with the recent ANTlabs Update #41 for both IG 4 and SG 4. Admins are advised to apply the latest update on their gateways to ensure a smoother login flow. After updating gateways to Update #41, using the Instagram login method […]
-
[UPDATED: 19 Jan 2021] WeChat login is now once again working as one of the ANTlabs social WiFi login methods. WeChat login requires the following update to be installed on these gateways: IG 4 Update #42 SG 4 Update #42 IG 4 S Series Update #4 SG 4 S Series Update #4 [Advisory Date: 20 […]